Что такое Malware (малварь) и как с этим бороться?
Malware или «Малварь», сокращенно от английского «malicious software» — вредоносное программное обеспечение, имеющее своей целью в той или иной форме нанести ущерб пользователю или компьютеру и его содержимому. Малварь — общее название для всех видов кибер-угроз, таких как: вирусы, трояны, шпионские программы, кейлоггеры, adware и др. Malware или вредоносы — достаточно распространенный вид кибер-угроз, и столкнуться с вредоносным ПО может каждый.
Какой вред может причинить Malware моему компьютеру?
Вредоносные программы создают множество проблем пользователю — от маленьких почти незаметных неудобств до серьезного финансового вреда:
- Меняют настройки браузера и не дают изменить их пользователю (например, устанавливает новую домашнюю страницу или поиск по умолчанию);
- Тратят ресурсы компьютера, тем самым снижают его быстродействие;
- Устанавливают рекламные программы на компьютер, такие как всплывающие окна и баннеры, которые работают даже без подключения к интернету;
- Используют компьютер и его ресурсы для DDoS-атак или майнинга криптовалют;
- Блокируют доступ к сайтам антивирусов и другим сайтам, содержащим инструменты для борьбы с вредоносным ПО;
- Собирают личные данные пользователя: логины, пароли, номера банковских карт и прочее;
- Без ведома пользователя могут скачивать с интернета и устанавливать другое вредоносное ПО.
Как удалить Malware с компьютера?
Такая программа хорошо маскируется и может ничем не выдавать свое присутствие для пользователя. Сегодня существует множество программных инструментов для того, чтобы очистить компьютер от Malware — антивирусы и специализированные Anti-Malware программы. Однако очень многие вредоносные программы (Malware) обладают настолько высокой степенью защиты, что их практически невозможно удалить после запуска.
Как SkyDNS блокирует доступ к ресурсам, содержащим Malware?
SkyDNS предлагает альтернативный способ избежать вредоносных программ. Наша система аналитики, основанная на принципах машинного обучения, позволяет с точностью до 98% определять ресурсы, содержащие вредоносное ПО и эффективно блокировать доступ к ним. Предотвратите негативное влияние Malware еще до того, как вредоносное программное обеспечение попадет на ваш компьютер. Предлагаем ознакомиться с популярными решениями для контент-фильтрации дома, в школе или в офисе от компании SkyDNS!
- Для дома
- Для бизнеса
- Для учебных заведений и библиотек
- Для провайдеров
- Для разработчиков
- Система аналитики SkyDNS Data
- Проверка безопасности
- О компании
- Контакты
- Партнерам
- Работа у нас
- Новости
- Условия использования
- Политика конфиденциальности
Malware.Heuristic.1003 Removal. Is It False Positive?
Malware.Heuristic.1003 is a detection present in Malwarebytes Anti-malware engine. It identifies a malicious item detected by a heuristic system. This system makes anti-malware solutions way more potent but is prone to false detections. To clear up whether it is hazardous or not, you should use another anti-malware software. Consider reading the article to see the details.
In the majority of the instances, Malware.Heuristic.1003 infection will advise its targets to initiate funds move for counteracting the modifications that the Trojan infection has actually presented to the victim’s tool.
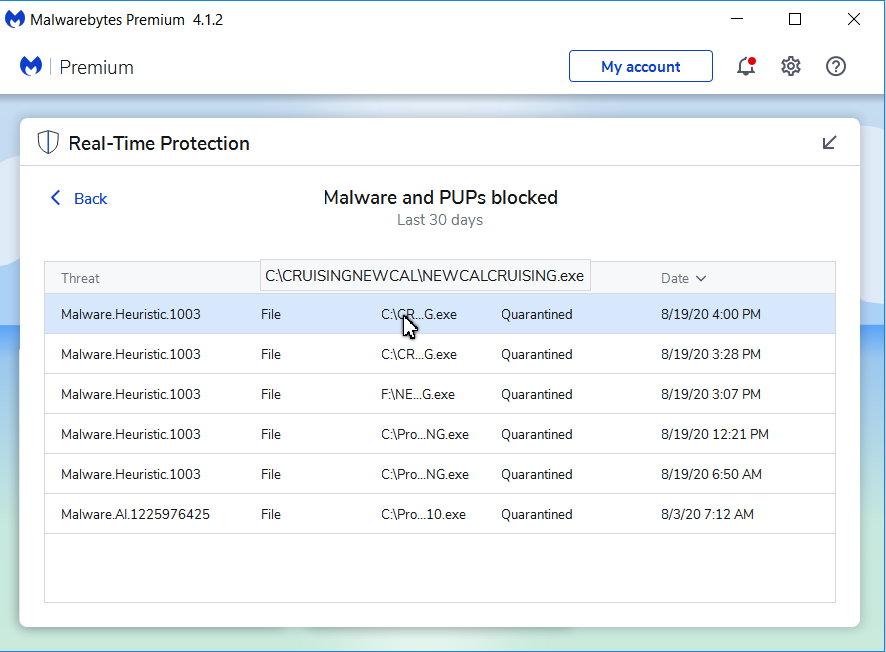
IrfanView, 7ZIP, Qbittorrent detected the latest version of Malwarebytes as “Malware.Heuristic.1003”
Robert Bailey
IT Security Expert
It is better to prevent, than repair and repent!
When we talk about the intrusion of unfamiliar programs into your computer’s work, the proverb «Forewarned is forearmed» describes the situation as accurately as possible. Gridinsoft Anti-Malware is exactly the tool that is always useful to have in your armory: fast, efficient, up-to-date. It is appropriate to use it as an emergency help at the slightest suspicion of infection.
Gridinsoft Anti-Malware 6-day trial available.
EULA | Privacy Policy | Gridinsoft
Subscribe to our Telegram channel to be the first to know about news and our exclusive materials on information security.
If Malware.Heuristic.1003 real threat
In cases when this refers to a real threat, the possible damage may be critical. Samples marked as Malware.Heuristic.1003 performs a row of malicious actions, that clearly show it is spyware.
List of malware actions
Click to view
- Executable code extraction.Cybercriminals often use binary packers to hinder the malicious code from being reverse-engineered by malware analysts. A packer is a tool that compresses, encrypts, and modifies a malicious file’s format.
- Injection (inter-process);
- Injection (Process Hollowing);
- Attempts to connect to a dead IP:Port (1 unique times);
- Creates RWX memory.There is a security trick with memory regions that allows an attacker to fill a buffer with a shellcode and then execute it.
- Possible date expiration check, exits too soon after checking local time;
- Reads data out of its own binary image.The trick that allows the malware to read data out of your computer’s memory. Everything you run, type, or click on your computer goes through the memory. This includes passwords, bank account numbers, emails, and other confidential information.
- Performs some HTTP requests;
- Unconventionial binary language: Russian;
- Unconventionial language used in binary resources: Russian;
- The binary likely contains encrypted or compressed data.In this case, encryption is a way of hiding virus’ code from antiviruses and virus’ analysts.
- The executable is compressed using UPX;
- Looks up the external IP address;
- Executed a process and injected code into it, probably while unpacking;
- Steals private information from local Internet browsers;
- Collects information about installed applications;
- Checks the CPU name from registry, possibly for anti-virtualization;
- Attempts to modify proxy settings.This trick used for inject malware into connection between browser and server;
- Attempts to access Bitcoin/ALTCoin wallets;
- Harvests information related to installed instant messenger clients;
- Collects information to fingerprint the system.There are behavioral human characteristics that can be used to digitally identify a person to grant access to systems, devices, or data. Unlike passwords and verification codes, fingerprints are fundamental parts of user’s identities.
Similar behavior
-
- Trojan-Banker.Win32.RTM.iho
- Win32/Kryptik.GYYR
- Win32/Spatet.C
Related domains
api.ipify.org Ransom.Phobos!8.10B6C (TFE:5:8mtWss1rAWC) Malware.Heuristic.1003
One of the most regular channels where Malware.Heuristic.1003 Virus are injected are:
- By means of phishing e-mails;
- Through cracked software, downloaded from third-party websites;
As soon as the Trojan is effectively injected, it will certainly either cipher the data on the victim’s PC or protect against the tool from functioning correctly – while likewise putting a ransom money note that states the need for the victims to effect the settlement for the objective of decrypting the files or restoring the file system to the first problem. In many circumstances, the ransom money note will turn up when the client restarts the computer after the system has actually currently been harmed.
Malware.Heuristic.1003 spreading ways
Currently, malware opts for pretty much same ways of spreading regardless of the country. Most popular options are email spam and pirated software. The former relies on users’ positive bias towards email messages – they simply don’t expect anything malicious to appear. Pirated a.k.a cracked programs, on the other hand, are illegal from the beginning. Burglars who hack them additionally embed malware in the package, so it is installing together with the crack.
Technical details
File information
Click to expand
crc32: 8079A784md5: a7d038f64060412d4726e8b8f3406821name: A7D038F64060412D4726E8B8F3406821.mlwsha1: b4c054da6b0734319e5ea08e23ca4fbbc95bcd43sha256: 8e4f25ae17e2868391994dee1de589d93b6162b085a726f76bd5b848330dd44dsha512: d12a2f20c285bdcb318f65dd368184f20cf1a475b671e0c4f049328359dc3fa9ec916ff1396d623e85d763f80c13ce02ea8b4a879cbf83522b334b3b62100a0assdeep: 24576:DVVE6YxK5X9bMFkrt9Acrr66LnQ3owApBK/RoNpyHiwpqBKzAWJ6Z+Dt+6Fw+ng:DVVE6YOX9bMFkrt9AcnNLnQaBK/qmiwEtype: MS-DOS executable
Version Info:
LegalCopyright: Copyright (C) 2021InternalName: e92FileVersion: 1, 0, 0, 1ProductName: e92 ApplicationProductVersion: 1, 0, 0, 1FileDescription: e92 ApplicationOriginalFilename: e92.exeTranslation: 0x0419 0x04b0Alternative detection names
Click to expand
Elastic malicious (high confidence) Qihoo-360 HEUR/QVM11.1.E2F1.Malware.Gen McAfee Artemis!A7D038F64060 AegisLab Trojan.Win32.Generic.4!c Sangfor Malware BitDefender Trojan.GenericKD.45632951 Cybereason malicious.a6b073 Symantec ML.Attribute.HighConfidence APEX Malicious Paloalto generic.ml Cynet Malicious (score: 90) Kaspersky Trojan-PSW.Win32.Ficker.hn MicroWorld-eScan Trojan.GenericKD.45632951 Rising Ransom.Phobos!8.10B6C (TFE:5:8mtWss1rAWC) Ad-Aware Trojan.GenericKD.45632951 McAfee-GW-Edition BehavesLike.Win32.Trojan.cc FireEye Generic.mg.a7d038f64060412d SentinelOne Static AI – Suspicious PE MAX malware (ai score=83) Kingsoft Win32.PSWTroj.Ficker.hn.(kcloud) Microsoft Trojan:Win32/Wacatac.B!ml ZoneAlarm Trojan-PSW.Win32.Ficker.hn GData Trojan.GenericKD.45632951 Malwarebytes Malware.Heuristic.1003 ESET-NOD32 a variant of Generik.IMAAQCJ Yandex Trojan.GenAsa!aY7wiZJpDug Ikarus Trojan.SuspectCRC BitDefenderTheta Gen:NN.ZexaF.34780.3mNfaO8Z1Rac AVG FileRepMalware Avast FileRepMalware How to remove Malware.Heuristic.1003 virus?
Unwanted application has ofter come with other viruses and spyware. This threats can steal account credentials, or crypt your documents for ransom.
Reasons why I would recommend GridinSoft 1
The is an excellent way to deal with recognizing and removing threats – using Gridinsoft Anti-Malware. This program will scan your PC, find and neutralize all suspicious processes. 2 .
Download GridinSoft Anti-Malware.
You can download GridinSoft Anti-Malware by clicking the button below:
Run the setup file.
When the setup file has finished downloading, double-click on the setup-antimalware-fix.exe file to install GridinSoft Anti-Malware on your system.
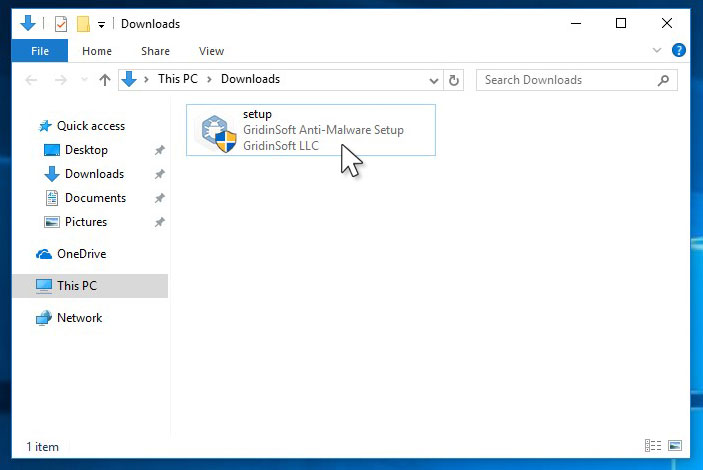
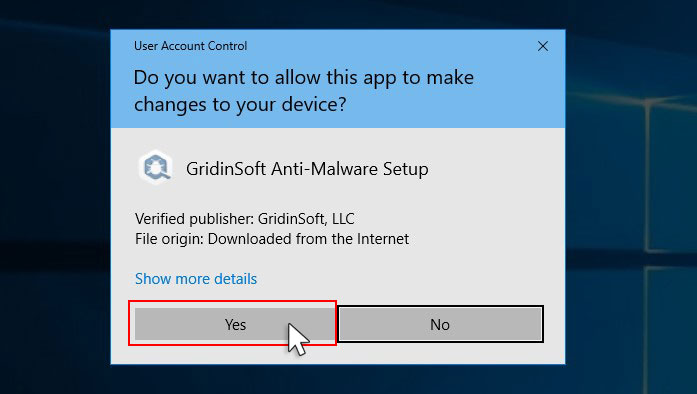
An User Account Control asking you about to allow GridinSoft Anti-Malware to make changes to your device. So, you should click “Yes” to continue with the installation.
Press “Install” button.
Once installed, Anti-Malware will automatically run.
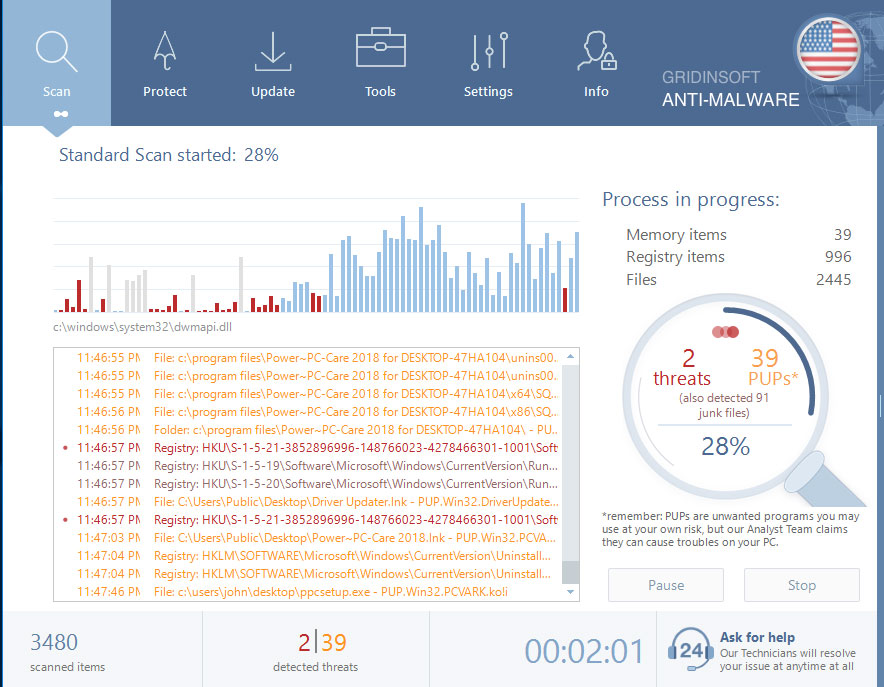
Wait for the Anti-Malware scan to complete.
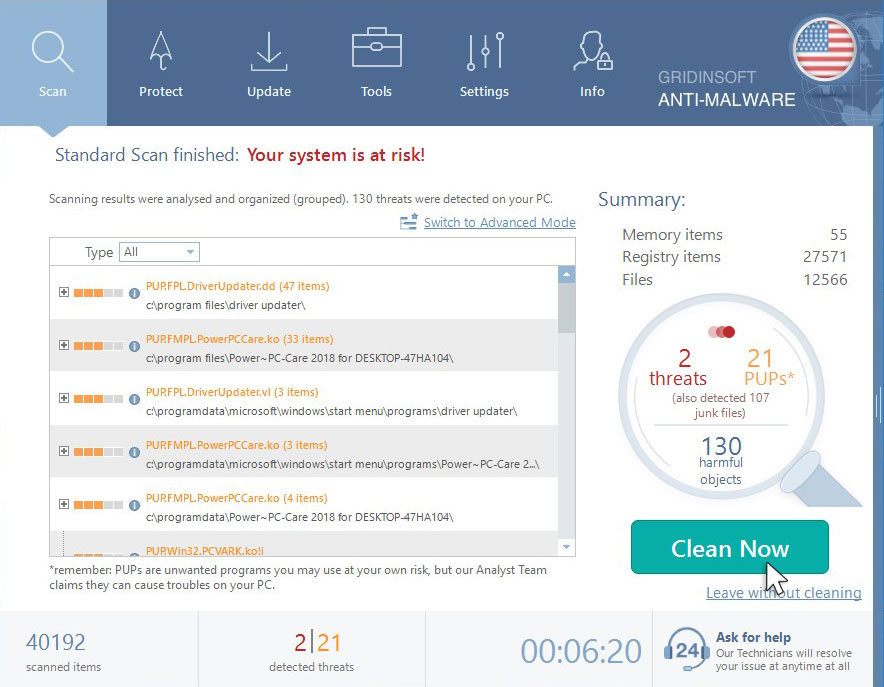
GridinSoft Anti-Malware will automatically start scanning your system for Malware.Heuristic.1003 files and other malicious programs. This process can take 20-30 minutes, so I suggest you periodically check on the status of the scan process.
Click on “Clean Now”.
When the scan has finished, you will see the list of infections that GridinSoft Anti-Malware has detected. To remove them click on the “Clean Now” button in the right corner.
Are Your Protected?
GridinSoft Anti-Malware will scan and clean your PC for free in the trial period. The free version offers real-time protection for the first 2 days. If you want to be fully protected at all times – I can be recommended you purchase a full version:
Full version of GridinSoft Anti-Malware
Suppose the guide doesn’t help you to remove Malware.Heuristic.1003 you can always ask me in the comments to get help.
Malware.Heuristic
Malware.Heuristic.(id-nr) are heuristic detection names produced by Malwarebytes 4 and Malwarebytes business products. The heuristic detections are done by non-signature based heuristics. This technique was developed by Malwarebytes for signatureless detection of zero-day (0-day) threats.
The id-nr is usually a few digits long.
Types of infection
Based on closer determination, items detected as Malware.Heuristic can be categorized more precisely based on their behavior. Malwarebytes uses the underlying threat categories:
- Adware
- Fraudtool
- Hijack
- Ransomware
- Riskware
- Rogue
- Rootkit
- Spyware
- Trojan
- Virus
- Worm
Protection
Malwarebytes detects unknown threats as Malware.Heuristic by using sandboxing and other emulation techniques without any specific detection rules to protect users from malware that has not yet been researched and classified. This helps protect our customers against 0-day malware.
что за угроза Malware.Heuristic!ET#100% (rdm+)
Троян. По названию .ехе ясно, что наставится куча хлама. ADW Cleaner, Malwarebytes Anti-Malware помогут после установки этого экзэшника.
Артур ЛошаринУченик (151) 3 года назад
brinГуру (2945) 2 года назад
Хаха, смешно.
Сам malwarebytes объявил файл — трояномОстальные ответы
рекламный модуль, может подменить адрес DNS сервера
рекламный модуль, может подменить адрес DNS сервера
Это хуже вируса. Она научит вас торговать на форексе.
Артур ЛошаринУченик (151) 3 года назад
рекламный модуль, может подменить адрес DNS сервера
Похожие вопросы
Ваш браузер устарел
Мы постоянно добавляем новый функционал в основной интерфейс проекта. К сожалению, старые браузеры не в состоянии качественно работать с современными программными продуктами. Для корректной работы используйте последние версии браузеров Chrome, Mozilla Firefox, Opera, Microsoft Edge или установите браузер Atom.