IDP.HEUR.25 это вирус или нет?
А кто его нашел?
HEUR — означает эристический анализ, предполагает что это что то вредоносное.
Егор РудьманПрофи (882) 1 год назад

Егор Рудьман, Тогда не ссы если Аваст ))
Похожие вопросы
Ваш браузер устарел
Мы постоянно добавляем новый функционал в основной интерфейс проекта. К сожалению, старые браузеры не в состоянии качественно работать с современными программными продуктами. Для корректной работы используйте последние версии браузеров Chrome, Mozilla Firefox, Opera, Microsoft Edge или установите браузер Atom.
IDP Generic — что это такое и стоит ли этого опасаться?
Во время установки/запуска того или иного приложения ваш антивирус может начать ругаться об угрозе в лице IDP Generic. Сегодня мы поведаем вам, что это за «зверь» такой и стоит ли его вообще бояться.
Что такое IDP Generic?
Главное — не паникуйте! Дайте угадаем: на вашем компьютере установлена бесплатная версия Avast или AVG? Если ответ — да, то вам не о чем переживать, потому как найденный файл с IDP Generic, скорее всего, является ложной тревогой.
Задокументировано бесчисленное количество случаев, когда подобные антивирусы находили IDP Generic в совершенно легальных и безопасных файлах. Например, некоторые пользователи утверждают, что у них данный вирус был обнаружен в только что загруженной игре из Steam. Как вы понимаете, это попросту невозможно.
Почему возникают эти ложные тревоги? Четкий ответ на этот вопрос дать сложно, но есть предположения, что причина — это устаревшая база данных бесплатного антивируса. Также не стоит исключать и простой баг. Так или иначе если вы уверены, что с файлом, помеченным IDP Generic, все нормально — верните его из карантина и добавьте в исключения. И обязательно не забудьте обновить свой антивирус!
Но вот куда более важный вопрос: а может IDP Generic быть не ложной тревогой, а реальной угрозой? Ответ — конечно же может. Если он был, к примеру, обнаружен в совершенно незнакомом для вас файле, который лежит где-то в недрах ОС Windows, — это может быть вирус! Установите на свой ПК антивирус понадежней (либо и вовсе воспользуйтесь Защитником Windows) и запустите глубокое сканирование системы, а затем избавьтесь от угрозы!
IDP.HEUR.25 Virus – How to Remove It
IDP.HEUR.25 is the name of a detection that has been reported to be either a false positive or malware-related. This software’s main purpose is so far unknown, but in case it turns out to be malware, then this may result in information that and even damages to your operating system. IDP.HEUR.25 has been reported to be related with multiple other types of detections, like IDP.ALEXA, which in some cases may turn out to be a dangerous Trojan horse.
Read this article to learn more about how IDP.HEUR.25 works, what are the risks of having it on your computer and how to remove it completely.

On this page:
IDP.HEUR.25 Summary
Malware Removal Tool
IDP.HEUR.25 Virus – More Information
IDP.HEUR.25 may pretend to be a lot of different applications to infect your computer, in case it is indeed malware. The software which it may imitate could be of the following kinds:
- Patches.
- Fake game or app installers.
- Cracks for games or other software.
- Updates.
- Portable programs.
These types of files may be hosted on some third-party websites which may promote them as useful applications that you may be looking to download for free.
Furthermore, reports indicate that applications, from the IDP.HEUR.25 kind have often been associated with the game crack of the Seamonkey game, as some of the files that are dropped from related deductions to this one I reported to contain the following names:
- Ammsetup(1).tmp
- Ammsetup.tmp
- Seamonkey.exe
These files could be located in different Windows directories, like the following ones:
- %AppData%
- %Local%
- %Temp%
- %LocalLow%
- %Roaming%
The consequences for your computer, in case IDP.HEUR.25 ends up being in the malware and not a false positive detection from Antivirus programs are many, for instance it may:
- Tamper with your hardware, which may result in the slowing down of your computer and ultimately lead to BSOD (blue screen of death).
- Delete important files from your PC, and this may include Windows system files.
- Grant hackers live access to your computer so they can see what you do.
- Download and install other software on your PC without your knowledge or consent.
- Get other details from your computer, such as system information..
These are the main reasons why this application is classified as dangerous for your computer system and should be getting rid of as soon as you see it.
IDP.HEUR.25 – How To Stop and Remove It
If you want to get rid of IDP.HEUR.25 from your computer, first you must determine where is files are located, using the information stated in the article above. Be advised, that the instructions underneath this article can help you in combination with this information to remove this malware manually. If you want a fast and effective solution that is also automatic, then we suggest that you follow experts recommendations and run a scan of your computer, using an advanced anti-malware software. Such a program is specifically created to run a thorough scan of your machine and detect and delete any malicious software completely.
Ventsislav Krastev
Ventsislav is a cybersecurity expert at SensorsTechForum since 2015. He has been researching, covering, helping victims with the latest malware infections plus testing and reviewing software and the newest tech developments. Having graduated Marketing as well, Ventsislav also has passion for learning new shifts and innovations in cybersecurity that become game changers. After studying Value Chain Management, Network Administration and Computer Administration of System Applications, he found his true calling within the cybersecrurity industry and is a strong believer in the education of every user towards online safety and security.

Follow Me:
Related posts:
- What Is IDP.ALEXA.51 and Should You Remove ItIDP.ALEXA.51 IDP.ALEXA.51 is a detection commonly linked to online games.
- IDP.ALEXA.53What Is IDP.ALEXA.53? Just like other detections of the IDP.ALEXA.
- IDP.HEUR.23 Virus RemovalWhat Is IDP.HEUR.23? IDP.HEUR.23 is the name of a detected.
- IDP.ALEXA.52 Virus Removal GUIDEIDP.ALEXA.52 is a virus detection primarily related to on the.
- IDP.Generic Virus Meaning – What Is It? [Removal Guide]What Is IDP.Generic IDP.Generic is a detection of a generic.
- Researchers Warn about Vulnerabilities in Alexa Skill EcosystemAmazon Alexa’s users should be aware of a new vulnerability.
- Alexa Is Spying on You to Help Amazon Improve ItSpecial team has been recently assigned in reviewing audio in.
- Car Hacking: Are Amazon’s New Automotive Products Secure?At this year’s Consumer Electronics Show (CES) 2020, Amazon announced.
Download (MAC)
Malware Removal Tool
Get a free scanner to see if your MAC is infected.
Use SpyHunter to remove malware in less than 15 minutes .
Enjoy a free 7-day trial using your credit card. Cancel at least two days before the trial ends to avoid any charges. Subscription fees vary by region and will renew automatically unless you cancel in time. You’ll receive a reminder before your next billing, and there’s a 30-day money-back guarantee. Read the full terms and discover the free removal service. Read more.
SPECIAL OFFER
Malware Removal Tool
Get a free scanner to see if your PC is infected.
SpyHunter 5 free remover allows you, subject to a 48-hour waiting period, one remediation and removal for results found. Read EULA and Privacy Policy
Preparation before removing IDP.HEUR.25.
Before starting the actual removal process, we recommend that you do the following preparation steps.
- Make sure you have these instructions always open and in front of your eyes.
- Do a backup of all of your files, even if they could be damaged. You should back up your data with a cloud backup solution and insure your files against any type of loss, even from the most severe threats.
- Be patient as this could take a while.
- Scan for Malware
- Fix Registries
- Remove Virus Files
Step 1: Scan for IDP.HEUR.25 with SpyHunter Anti-Malware Tool
1. Click on the «Download» button to proceed to SpyHunter’s download page.
Malware Removal Tool
It is recommended to run a scan before purchasing the full version of the software to make sure that the current version of the malware can be detected by SpyHunter. Click on the corresponding links to check SpyHunter’s EULA, Privacy Policy and Threat Assessment Criteria.
2. After you have installed SpyHunter, wait for it to update automatically.
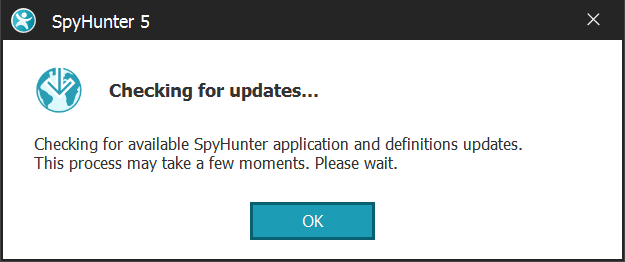
3. After the update process has finished, click on the ‘Malware/PC Scan’ tab. A new window will appear. Click on ‘Start Scan’.

4. After SpyHunter has finished scanning your PC for any files of the associated threat and found them, you can try to get them removed automatically and permanently by clicking on the ‘Next’ button.

If any threats have been removed, it is highly recommended to restart your PC.
Step 2: Clean any registries, created by IDP.HEUR.25 on your computer.
The usually targeted registries of Windows machines are the following:
- HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\Run
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run
- HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\RunOnce
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\RunOnce
You can access them by opening the Windows registry editor and deleting any values, created by IDP.HEUR.25 there. This can happen by following the steps underneath:
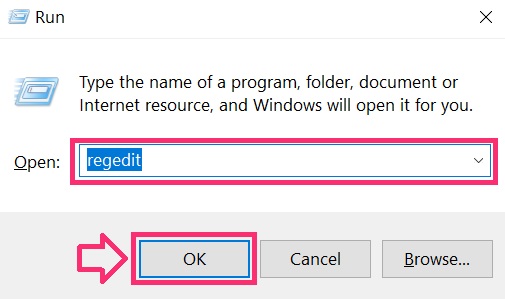
1. Open the Run Window again, type «regedit» and click OK.
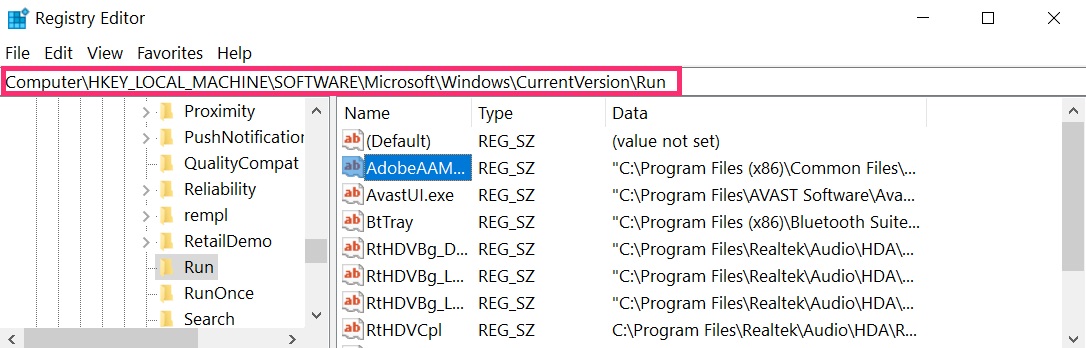
2. When you open it, you can freely navigate to the Run and RunOnce keys, whose locations are shown above.
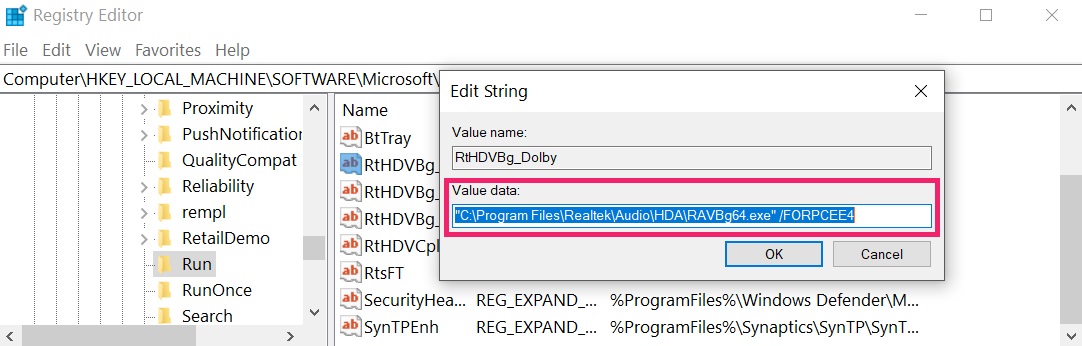
3. You can remove the value of the virus by right-clicking on it and removing it. Tip: To find a virus-created value, you can right-click on it and click «Modify» to see which file it is set to run. If this is the virus file location, remove the value.
Step 3: Find virus files created by IDP.HEUR.25 on your PC.
1.For Windows 8, 8.1 and 10.
For Newer Windows Operating Systems
1: On your keyboard press + R and write explorer.exe in the Run text box and then click on the Ok button.

2: Click on your PC from the quick access bar. This is usually an icon with a monitor and its name is either “My Computer”, “My PC” or “This PC” or whatever you have named it.

3: Navigate to the search box in the top-right of your PC’s screen and type “fileextension:” and after which type the file extension. If you are looking for malicious executables, an example may be «fileextension:exe». After doing that, leave a space and type the file name you believe the malware has created. Here is how it may appear if your file has been found:

N.B. We recommend to wait for the green loading bar in the navigation box to fill up in case the PC is looking for the file and hasn’t found it yet.
2.For Windows XP, Vista, and 7.
For Older Windows Operating Systems
In older Windows OS’s the conventional approach should be the effective one:
1: Click on the Start Menu icon (usually on your bottom-left) and then choose the Search preference.

2: After the search window appears, choose More Advanced Options from the search assistant box. Another way is by clicking on All Files and Folders.
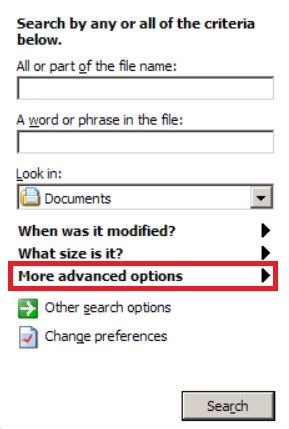
3: After that type the name of the file you are looking for and click on the Search button. This might take some time after which results will appear. If you have found the malicious file, you may copy or open its location by right-clicking on it.
Now you should be able to discover any file on Windows as long as it is on your hard drive and is not concealed via special software.
IDP.HEUR.25 FAQ
What Does IDP.HEUR.25 Trojan Do?
The IDP.HEUR.25 Trojan is a malicious computer program designed to disrupt, damage, or gain unauthorized access to a computer system.
It can be used to steal sensitive data, gain control over a system, or launch other malicious activities.
What Damage Can IDP.HEUR.25 Trojan Cause?
The IDP.HEUR.25 Trojan is a malicious type of malware that can cause significant damage to computers, networks and data.
It can be used to steal information, take control of systems, and spread other malicious viruses and malware.
Is IDP.HEUR.25 Trojan a Harmful Virus?
Yes, it is. A Trojan is a type of malicious software that is used to gain unauthorized access to a person’s device or system. It can damage files, delete data, and even steal confidential information.
Can Trojans Steal Passwords?
Yes, Trojans, like IDP.HEUR.25, can steal passwords. These malicious programs are designed to gain access to a user’s computer, spy on victims and steal sensitive information such as banking details and passwords.
Can IDP.HEUR.25 Trojan Hide Itself?
Yes, it can. A Trojan can use various techniques to mask itself, including rootkits, encryption, and obfuscation, to hide from security scanners and evade detection.
Can a Trojan be Removed by Factory Reset?
Yes, a Trojan can be removed by factory resetting your device. This is because it will restore the device to its original state, eliminating any malicious software that may have been installed.
Can IDP.HEUR.25 Trojan Infect WiFi?
Yes, it is possible for a Trojan to infect WiFi networks. When a user connects to the infected network, the Trojan can spread to other connected devices and can access sensitive information on the network.
Can Trojans Be Deleted?
Yes, Trojans can be deleted. This is typically done by running a powerful anti-virus or anti-malware program that is designed to detect and remove malicious files. In some cases, manual deletion of the Trojan may also be necessary.
Can Trojans Steal Files?
Yes, Trojans can steal files if they are installed on a computer. This is done by allowing the malware author or user to gain access to the computer and then steal the files stored on it.
Which Anti-Malware Can Remove Trojans?
Anti-malware programs such as SpyHunter are capable of scanning for and removing Trojans from your computer. It is important to keep your anti-malware up to date and regularly scan your system for any malicious software.
Can Trojans Infect USB?
Yes, Trojans can infect USB devices. USB Trojans typically spread through malicious files downloaded from the internet or shared via email, allowing the hacker to gain access to a user’s confidential data.
About the IDP.HEUR.25 Research
The content we publish on SensorsTechForum.com, this IDP.HEUR.25 how-to removal guide included, is the outcome of extensive research, hard work and our team’s devotion to help you remove the specific trojan problem.
How did we conduct the research on IDP.HEUR.25?
Please note that our research is based on an independent investigation. We are in contact with independent security researchers, thanks to which we receive daily updates on the latest malware definitions, including the various types of trojans (backdoor, downloader, infostealer, ransom, etc.)
Furthermore, the research behind the IDP.HEUR.25 threat is backed with VirusTotal.
To better understand the threat posed by trojans, please refer to the following articles which provide knowledgeable details.
Бесконечное открывание новых вкладок в Firefox и Chrome [HEUR:Trojan.Script.Generic, HEUR:Trojan.Win32.Agent.gen] (заявка № 222547)


Junior Member Регистрация 18.04.2019 Сообщений 9 Вес репутации 18
 Бесконечное открывание новых вкладок в Firefox и Chrome [HEUR:Trojan.Script.Generic, HEUR:Trojan.Win32.Agent.gen]
Здравствуйте!
Прошу помощи, ибо ничего не помогает, а проблема очень серьёзная и назойливая.
Накануне скачала с виду нормальный файл, который по факту оказался ящиком Пандоры с вирусами.
Благодаря нему теперь с частотой от 2 секунд до нескольких минут в «Firefox» и «Chrome» открывается уйма вкладок с разными сайтами, но редирект идёт от thegoodcaster(.com). Периодически также вылезает приложение «One System Care» (которое я не устанавливала самостоятельно) и идёт попытка установки каких-то новых приложений.
Неоднократно прогоняла систему через «Dr. Web CureIt», «AdwCleaner» и «Spybot — Search&Destroy». Ничего не помогло. Они вроде что-то находят, удаляют, перемещают, но после перезагрузки компьютера всё начинается заново (причём автозапуском). Поиск и удаление подозрительных задач в планировщике также не принёс особых результатов. Самостоятельное вычисление сторонних файлов в папках «Windows», «Program Files» и «AppData» в общем-то завершились успешно, но вот удаление этих сторонних файлов вручную не получилось — система выдала что-то вроде ошибки доступа.
На данный момент подозрительными, но не удалёнными остаются:
— Приложения «One System Care», «Gerpril», «TrustedInstaller», H25MF9DDA.exe, TBFMIWCXV2.exe, ER6MNWIGP.exe, wscript.exe, appcmd.exe
— wsclient.dll, apphostsvc.dll, appobj.dll, certobj.dll, iisreg.dll и так далее
— Процесс? Программы? — HotStart и aspnetca (ASP.NET)
— Папки «SysWOW64» и «Prefetch» в «Windows»
И ещё: попытка соединиться с нормальными сайтами оканчивается также ничем — соединение отстутствует, при том что другие, «левые» сайты отлично загружаются.
Логи из «AutoLogger», а также некоторые скриншоты прикрепляю.
P.S. Слава богу, что есть ещё один компьютер, с которого можно связаться с миром

Изображения
- 2019-04-18_09-53-19.png (14.5 Кб, 2 просмотров)
- 2019-04-18_09-41-32.png (12.6 Кб, 3 просмотров)
Будь в курсе! Будь в курсе!
Надоело быть жертвой? Стань профи по информационной безопасности, получай самую свежую информацию об угрозах и средствах защиты от ведущего российского аналитического центра Anti-Malware.ru:
18.04.2019, 12:18 #2
Cyber  Регистрация 11.05.2011 Сообщений 2,284 Вес репутации 376
Уважаемый(ая) EwGene, спасибо за обращение на наш форум!
Удаление вирусов — абсолютно бесплатная услуга на VirusInfo.Info. Хелперы в самое ближайшее время ответят на Ваш запрос. Для оказания помощи необходимо предоставить логи сканирования утилитой Autologger, подробнее можно прочитать в правилах оформления запроса о помощи.
Информация
Если вы хотите получить персональную гарантированную помощь в приоритетном режиме, то воспользуйтесь платным сервисом Помогите+.
Если наш сайт окажется полезен Вам и у Вас будет такая возможность — пожалуйста поддержите проект.
18.04.2019, 22:56 #3
Senior Helper Регистрация 06.05.2008 Адрес Тула Сообщений 35,286 Вес репутации 1054
Не то выложили, правила перечитайте.
18.04.2019, 23:20 #4
Junior Member Регистрация 18.04.2019 Сообщений 9 Вес репутации 18
Да, извините.
Вот то, что нужно.
Вложения
- CollectionLog-2019.04.18-10.58.zip (97.2 Кб, 1 просмотров)
19.04.2019, 10:49 #5
Senior Helper Регистрация 06.05.2008 Адрес Тула Сообщений 35,286 Вес репутации 1054
Запустите HijackThis, расположенный в папке Autologger (в Windows Vista/7/8/10 необходимо запускать через правую кнопку мыши Запуск от имени администратора))и пофиксите только эти строки:
O15 - Trusted Zone: https://vk-local-server.cezurity.com O17 - DHCP DNS 1: 116.202.1.65 O17 - HKLM\System\CCS\Services\Tcpip\..\: [NameServer] = 116.202.1.65 O17 - HKLM\System\CCS\Services\Tcpip\..\: [NameServer] = 116.202.1.65 O22 - Task: Adobe Flash Player NPAPI Notifier - C:\WINDOWS\SysWOW64\Macromed\Flash\FlashUtil32_32_0_0_171_Plugin.exe -check plugin (file missing) O22 - Task: GoogleUpdateTaskMachineCore - C:\Program Files (x86)\Google\Update\GoogleUpdate.exe /c (file missing) O22 - Task: GoogleUpdateTaskMachineUA - C:\Program Files (x86)\Google\Update\GoogleUpdate.exe /ua /installsource scheduler (file missing) O22 - Task: Norton WSC Integration - C:\Program Files (x86)\Norton Internet Security\Engine\22.9.4.8\WSCStub.exe /taskschd (file missing) O22 - Task: \Norton Internet Security\Norton Internet Security Error Analyzer - C:\Program Files (x86)\Norton Internet Security\Engine\22.9.4.8\SymErr.exe /analyze (file missing) O22 - Task: \Norton Internet Security\Norton Internet Security Error Processor - C:\Program Files (x86)\Norton Internet Security\Engine\22.9.4.8\SymErr.exe /submit (file missing)
begin ExecuteFile('net.exe', 'stop tcpip /y', 0, 15000, true); TerminateProcessByName('C:\Program Files (x86)\Rotation\428190386.exe'); TerminateProcessByName('C:\Program Files (x86)\Rotation\612377947.exe'); TerminateProcessByName('C:\Program Files\Hewlett-Packard\3XVSILJ8P53GRG\kXLHCink8w.exe'); TerminateProcessByName('c:\users\0982~1\appdata\local\temp\is-13qpb.tmp\awhtrevkxf0.tmp'); TerminateProcessByName('c:\users\0982~1\appdata\local\temp\is-51mhv.tmp\1bei5fvhd3b.tmp'); TerminateProcessByName('c:\users\0982~1\appdata\local\temp\is-9oea2.tmp\khmgohgycfm.tmp'); TerminateProcessByName('c:\users\0982~1\appdata\local\temp\is-da6rb.tmp\lczuaazddk1.tmp'); TerminateProcessByName('c:\users\0982~1\appdata\local\temp\is-ddnj3.tmp\l045jjx0cxi.tmp'); TerminateProcessByName('c:\users\0982~1\appdata\local\temp\is-ds1bb.tmp\zhtnfrcltd2.tmp'); TerminateProcessByName('c:\users\0982~1\appdata\local\temp\is-est3t.tmp\ixcynhtlkw3.tmp'); TerminateProcessByName('c:\users\0982~1\appdata\local\temp\is-m9hd2.tmp\pt0rp2kgxhp.tmp'); TerminateProcessByName('c:\users\0982~1\appdata\local\temp\is-rlr67.tmp\1g5nrcjsnkn.tmp'); TerminateProcessByName('c:\users\Женя\appdata\roaming\002ejuwlyrd\pt0rp2kgxhp.exe'); TerminateProcessByName('c:\users\Женя\appdata\roaming\bidfl1prcca\l045jjx0cxi.exe'); TerminateProcessByName('c:\users\Женя\appdata\roaming\byxvokhwjlo\lczuaazddk1.exe'); TerminateProcessByName('c:\users\Женя\appdata\roaming\czmtnotjlx2\awhtrevkxf0.exe'); TerminateProcessByName('c:\users\Женя\appdata\roaming\ezx1g2keys5\ixcynhtlkw3.exe'); TerminateProcessByName('c:\users\Женя\appdata\roaming\j45trjrrnxu\1g5nrcjsnkn.exe'); TerminateProcessByName('c:\users\Женя\appdata\roaming\ly1zn1dznpz\zhtnfrcltd2.exe'); TerminateProcessByName('c:\users\Женя\appdata\roaming\n4vz3enxmkl\1bei5fvhd3b.exe'); TerminateProcessByName('c:\users\Женя\appdata\roaming\sbznvpi10sk\khmgohgycfm.exe'); StopService('rcdll'); QuarantineFile('C:\Program Files (x86)\Rotation\428190386.exe', ''); QuarantineFile('C:\Program Files (x86)\Rotation\612377947.exe', ''); QuarantineFile('C:\Program Files (x86)\yXYMSblVdIE\kf9eOEHK.dll', ''); QuarantineFile('C:\Program Files\Hewlett-Packard\3XVSILJ8P53GRG\#gRYDWjxe4.exe', ''); QuarantineFile('C:\Program Files\Hewlett-Packard\3XVSILJ8P53GRG\kXLHCink8w.exe', ''); QuarantineFile('c:\users\0982~1\appdata\local\temp\is-13qpb.tmp\awhtrevkxf0.tmp', ''); QuarantineFile('C:\Users\0982~1\AppData\Local\Temp\is-4JTGL.tmp\_isetup\_isdecmp.dll', ''); QuarantineFile('C:\Users\0982~1\AppData\Local\Temp\is-4JTGL.tmp\idp.dll', ''); QuarantineFile('c:\users\0982~1\appdata\local\temp\is-51mhv.tmp\1bei5fvhd3b.tmp', ''); QuarantineFile('c:\users\0982~1\appdata\local\temp\is-9oea2.tmp\khmgohgycfm.tmp', ''); QuarantineFile('C:\Users\0982~1\AppData\Local\Temp\is-A4FHR.tmp\_isetup\_isdecmp.dll', ''); QuarantineFile('C:\Users\0982~1\AppData\Local\Temp\is-A4FHR.tmp\idp.dll', ''); QuarantineFile('C:\Users\0982~1\AppData\Local\Temp\is-BHLB3.tmp\_isetup\_isdecmp.dll', ''); QuarantineFile('C:\Users\0982~1\AppData\Local\Temp\is-BHLB3.tmp\idp.dll', ''); QuarantineFile('c:\users\0982~1\appdata\local\temp\is-da6rb.tmp\lczuaazddk1.tmp', ''); QuarantineFile('c:\users\0982~1\appdata\local\temp\is-ddnj3.tmp\l045jjx0cxi.tmp', ''); QuarantineFile('c:\users\0982~1\appdata\local\temp\is-ds1bb.tmp\zhtnfrcltd2.tmp', ''); QuarantineFile('c:\users\0982~1\appdata\local\temp\is-est3t.tmp\ixcynhtlkw3.tmp', ''); QuarantineFile('C:\Users\0982~1\AppData\Local\Temp\is-JT3LN.tmp\_isetup\_isdecmp.dll', ''); QuarantineFile('C:\Users\0982~1\AppData\Local\Temp\is-JT3LN.tmp\idp.dll', ''); QuarantineFile('c:\users\0982~1\appdata\local\temp\is-m9hd2.tmp\pt0rp2kgxhp.tmp', ''); QuarantineFile('C:\Users\0982~1\AppData\Local\Temp\is-OR5M4.tmp\_isetup\_isdecmp.dll', ''); QuarantineFile('C:\Users\0982~1\AppData\Local\Temp\is-OR5M4.tmp\idp.dll', ''); QuarantineFile('C:\Users\0982~1\AppData\Local\Temp\is-P2ULT.tmp\_isetup\_isdecmp.dll', ''); QuarantineFile('C:\Users\0982~1\AppData\Local\Temp\is-P2ULT.tmp\idp.dll', ''); QuarantineFile('C:\Users\0982~1\AppData\Local\Temp\is-RKIUU.tmp\_isetup\_isdecmp.dll', ''); QuarantineFile('C:\Users\0982~1\AppData\Local\Temp\is-RKIUU.tmp\idp.dll', ''); QuarantineFile('c:\users\0982~1\appdata\local\temp\is-rlr67.tmp\1g5nrcjsnkn.tmp', ''); QuarantineFile('C:\Users\0982~1\AppData\Local\Temp\is-RO3MM.tmp\_isetup\_isdecmp.dll', ''); QuarantineFile('C:\Users\0982~1\AppData\Local\Temp\is-RO3MM.tmp\idp.dll', ''); QuarantineFile('C:\Users\0982~1\AppData\Local\Temp\is-UON8P.tmp\_isetup\_isdecmp.dll', ''); QuarantineFile('C:\Users\0982~1\AppData\Local\Temp\is-UON8P.tmp\idp.dll', ''); QuarantineFile('C:\Users\0982~1\AppData\Local\Temp\rcdll.exe', ''); QuarantineFile('c:\users\Женя\appdata\roaming\002ejuwlyrd\pt0rp2kgxhp.exe', ''); QuarantineFile('c:\users\Женя\appdata\roaming\bidfl1prcca\l045jjx0cxi.exe', ''); QuarantineFile('c:\users\Женя\appdata\roaming\byxvokhwjlo\lczuaazddk1.exe', ''); QuarantineFile('c:\users\Женя\appdata\roaming\czmtnotjlx2\awhtrevkxf0.exe', ''); QuarantineFile('c:\users\Женя\appdata\roaming\ezx1g2keys5\ixcynhtlkw3.exe', ''); QuarantineFile('c:\users\Женя\appdata\roaming\j45trjrrnxu\1g5nrcjsnkn.exe', ''); QuarantineFile('c:\users\Женя\appdata\roaming\ly1zn1dznpz\zhtnfrcltd2.exe', ''); QuarantineFile('c:\users\Женя\appdata\roaming\n4vz3enxmkl\1bei5fvhd3b.exe', ''); QuarantineFile('c:\users\Женя\appdata\roaming\sbznvpi10sk\khmgohgycfm.exe', ''); DeleteFile('C:\Program Files (x86)\Rotation\428190386.exe', ''); DeleteFile('C:\Program Files (x86)\Rotation\612377947.exe', ''); DeleteFile('C:\Program Files (x86)\Rotation\428190386.exe', '64'); DeleteFile('C:\Program Files (x86)\Rotation\612377947.exe', '64'); DeleteFile('C:\Program Files (x86)\yXYMSblVdIE\kf9eOEHK.dll', ''); DeleteFile('C:\Program Files\Hewlett-Packard\3XVSILJ8P53GRG\#gRYDWjxe4.exe', '64'); DeleteFile('C:\Program Files\Hewlett-Packard\3XVSILJ8P53GRG\kXLHCink8w.exe', ''); DeleteFile('c:\users\0982~1\appdata\local\temp\is-13qpb.tmp\awhtrevkxf0.tmp', ''); DeleteFile('C:\Users\0982~1\AppData\Local\Temp\is-4JTGL.tmp\_isetup\_isdecmp.dll', ''); DeleteFile('C:\Users\0982~1\AppData\Local\Temp\is-4JTGL.tmp\idp.dll', ''); DeleteFile('c:\users\0982~1\appdata\local\temp\is-51mhv.tmp\1bei5fvhd3b.tmp', ''); DeleteFile('c:\users\0982~1\appdata\local\temp\is-9oea2.tmp\khmgohgycfm.tmp', ''); DeleteFile('C:\Users\0982~1\AppData\Local\Temp\is-A4FHR.tmp\_isetup\_isdecmp.dll', ''); DeleteFile('C:\Users\0982~1\AppData\Local\Temp\is-A4FHR.tmp\idp.dll', ''); DeleteFile('C:\Users\0982~1\AppData\Local\Temp\is-BHLB3.tmp\_isetup\_isdecmp.dll', ''); DeleteFile('C:\Users\0982~1\AppData\Local\Temp\is-BHLB3.tmp\idp.dll', ''); DeleteFile('c:\users\0982~1\appdata\local\temp\is-da6rb.tmp\lczuaazddk1.tmp', ''); DeleteFile('c:\users\0982~1\appdata\local\temp\is-ddnj3.tmp\l045jjx0cxi.tmp', ''); DeleteFile('c:\users\0982~1\appdata\local\temp\is-ds1bb.tmp\zhtnfrcltd2.tmp', ''); DeleteFile('c:\users\0982~1\appdata\local\temp\is-est3t.tmp\ixcynhtlkw3.tmp', ''); DeleteFile('C:\Users\0982~1\AppData\Local\Temp\is-JT3LN.tmp\_isetup\_isdecmp.dll', ''); DeleteFile('C:\Users\0982~1\AppData\Local\Temp\is-JT3LN.tmp\idp.dll', ''); DeleteFile('c:\users\0982~1\appdata\local\temp\is-m9hd2.tmp\pt0rp2kgxhp.tmp', ''); DeleteFile('C:\Users\0982~1\AppData\Local\Temp\is-OR5M4.tmp\_isetup\_isdecmp.dll', ''); DeleteFile('C:\Users\0982~1\AppData\Local\Temp\is-OR5M4.tmp\idp.dll', ''); DeleteFile('C:\Users\0982~1\AppData\Local\Temp\is-P2ULT.tmp\_isetup\_isdecmp.dll', ''); DeleteFile('C:\Users\0982~1\AppData\Local\Temp\is-P2ULT.tmp\idp.dll', ''); DeleteFile('C:\Users\0982~1\AppData\Local\Temp\is-RKIUU.tmp\_isetup\_isdecmp.dll', ''); DeleteFile('C:\Users\0982~1\AppData\Local\Temp\is-RKIUU.tmp\idp.dll', ''); DeleteFile('c:\users\0982~1\appdata\local\temp\is-rlr67.tmp\1g5nrcjsnkn.tmp', ''); DeleteFile('C:\Users\0982~1\AppData\Local\Temp\is-RO3MM.tmp\_isetup\_isdecmp.dll', ''); DeleteFile('C:\Users\0982~1\AppData\Local\Temp\is-RO3MM.tmp\idp.dll', ''); DeleteFile('C:\Users\0982~1\AppData\Local\Temp\is-UON8P.tmp\_isetup\_isdecmp.dll', ''); DeleteFile('C:\Users\0982~1\AppData\Local\Temp\is-UON8P.tmp\idp.dll', ''); DeleteFile('C:\Users\0982~1\AppData\Local\Temp\rcdll.exe', ''); DeleteFile('c:\users\Женя\appdata\roaming\002ejuwlyrd\pt0rp2kgxhp.exe', ''); DeleteFile('c:\users\Женя\appdata\roaming\bidfl1prcca\l045jjx0cxi.exe', ''); DeleteFile('c:\users\Женя\appdata\roaming\byxvokhwjlo\lczuaazddk1.exe', ''); DeleteFile('c:\users\Женя\appdata\roaming\czmtnotjlx2\awhtrevkxf0.exe', ''); DeleteFile('c:\users\Женя\appdata\roaming\ezx1g2keys5\ixcynhtlkw3.exe', ''); DeleteFile('c:\users\Женя\appdata\roaming\j45trjrrnxu\1g5nrcjsnkn.exe', ''); DeleteFile('c:\users\Женя\appdata\roaming\ly1zn1dznpz\zhtnfrcltd2.exe', ''); DeleteFile('c:\users\Женя\appdata\roaming\n4vz3enxmkl\1bei5fvhd3b.exe', ''); DeleteFile('c:\users\Женя\appdata\roaming\sbznvpi10sk\khmgohgycfm.exe', ''); DeleteFile('C:\Users\Женя\Favorites\Links\Интернет.url'); DeleteService('gupdate'); DeleteService('gupdatem'); DeleteService('rcdll'); DeleteFileMask('c:\program files (x86)\yxymsblvdie', '*', true); DeleteFileMask('c:\program files\hewlett-packard\3xvsilj8p53grg', '*', true); DeleteFileMask('c:\users\женя\appdata\roaming\002ejuwlyrd', '*', true); DeleteFileMask('c:\users\женя\appdata\roaming\bidfl1prcca', '*', true); DeleteFileMask('c:\users\женя\appdata\roaming\byxvokhwjlo', '*', true); DeleteFileMask('c:\users\женя\appdata\roaming\czmtnotjlx2', '*', true); DeleteFileMask('c:\users\женя\appdata\roaming\ezx1g2keys5', '*', true); DeleteFileMask('c:\users\женя\appdata\roaming\j45trjrrnxu', '*', true); DeleteFileMask('c:\users\женя\appdata\roaming\ly1zn1dznpz', '*', true); DeleteFileMask('c:\users\женя\appdata\roaming\n4vz3enxmkl', '*', true); DeleteFileMask('c:\users\женя\appdata\roaming\sbznvpi10sk', '*', true); DeleteDirectory('c:\program files (x86)\yxymsblvdie'); DeleteDirectory('c:\program files\hewlett-packard\3xvsilj8p53grg'); DeleteDirectory('c:\users\женя\appdata\roaming\002ejuwlyrd'); DeleteDirectory('c:\users\женя\appdata\roaming\bidfl1prcca'); DeleteDirectory('c:\users\женя\appdata\roaming\byxvokhwjlo'); DeleteDirectory('c:\users\женя\appdata\roaming\czmtnotjlx2'); DeleteDirectory('c:\users\женя\appdata\roaming\ezx1g2keys5'); DeleteDirectory('c:\users\женя\appdata\roaming\j45trjrrnxu'); DeleteDirectory('c:\users\женя\appdata\roaming\ly1zn1dznpz'); DeleteDirectory('c:\users\женя\appdata\roaming\n4vz3enxmkl'); DeleteDirectory('c:\users\женя\appdata\roaming\sbznvpi10sk'); DelBHO(''); RegKeyParamDel('HKEY_LOCAL_MACHINE', 'Software\Microsoft\Windows\CurrentVersion\RunOnce', '4zsdsc4g3x3'); RegKeyParamDel('HKEY_LOCAL_MACHINE', 'Software\Microsoft\Windows\CurrentVersion\RunOnce', 'novmvun3z0l'); RegKeyParamDel('HKEY_LOCAL_MACHINE', 'Software\Microsoft\Windows\CurrentVersion\RunOnce', 'OMEWPRODUCT_'); CreateQurantineArchive(GetAVZDirectory + 'quarantine.zip'); ExecuteSysClean; ExecuteRepair(21); ExecuteWizard('SCU', 2, 2, true); RebootWindows(true); end.
В папке с AVZ появится архив карантина quarantine.zip, отправьте этот файл по ссылке «Прислать запрошенный карантин» над над первым сообщением в теме.
Удалите Spybot — Search & Destroy.